

Salesforce Authenticator
by Salesforce.com, inc.
4.4
- Safety
- 100% Safe
- Category
- Business
- Ratings
- 4.4
- Price
- Free
- Download
- 5.00M
This app is secure, reliable, free to install, and offers fast downloads without any risks or malware.
Screenshots
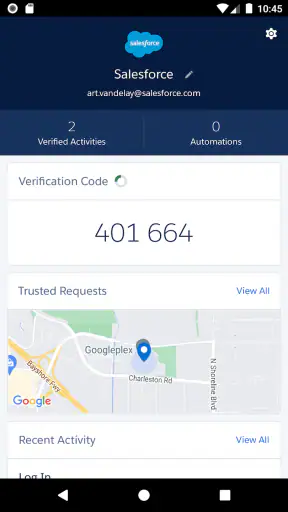
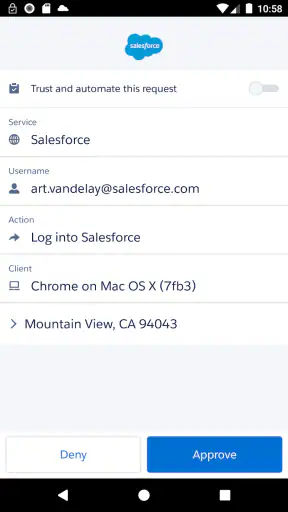
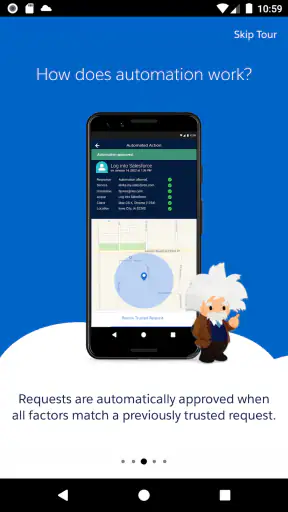
 Analysis by Getfullapps
Account security is easiest to appreciate when it fits into the routine you already follow. That is where Salesforce Authenticator makes sense: it is a business-focused app from Salesforce.com, inc. that adds a second verification step when you sign in. I found it most useful when I treated it as part of my normal login habit rather than as another security tool to open only during emergencies.
The app is free, rated for Everyone, and belongs to the business category. It has been available since November 4, 2013, and the current version is 4.8.0 for devices running iOS 9 or later. Its average rating is 4.4 from around 27 thousand ratings, with over 5 million installs, so it is clearly used beyond a small group of Salesforce administrators.
Building a safer sign-in routine around the app
Once the app is part of my routine, I treat each approval as a small identity check rather than a notification to clear. I also find it useful to decide ahead of time what I will do if a request arrives while I am away from my work screen: pause, verify whether I started the sign-in, and seek help if the situation remains unclear. That habit leads naturally to the next question: how to make the surrounding sign-in routine dependable.
Start with the workflow before installing anything
A second factor works best when I first understand which account or workplace service it protects. Salesforce Authenticator is not a general password manager, and it does not replace the password or sign-in details for the service being protected. Its role is narrower and clearer: it helps confirm that the person attempting a login is really the account holder.
That distinction matters in a busy workday. If I am signing in to a company Salesforce account from a new browser, the password is only one part of the process. The authenticator adds another checkpoint. This makes stolen or guessed passwords less useful on their own, but it also means I need access to the device where the authentication request arrives.
Before relying on it, I would make the setup part of an intentional account-security session. Install the app, connect it to the supported work account through the organization’s sign-in process, and complete a test login while I still have access to help from an administrator or support contact. Doing this during a calm moment is much better than discovering a setup problem just before an important meeting.
My practical recommendation is to decide in advance what “normal” looks like. A login from my usual laptop at a familiar time should be easy to recognize. A prompt that appears when I am not signing in deserves a pause rather than an automatic approval. The most important habit is refusing unexpected authentication requests, because a second factor only helps when I use it as a verification decision, not as a button to press blindly.
Articles to Explore Next

Uber Eats Makes Dinner Easier to Manage, but the Fees Add Up

Google Photos Turns a Camera Roll Into a Library You Can Find Your Way Through

Canva on Mobile: Adopt It for Quick Visuals, Test It for Demanding Work

Google Drive Keeps Work Moving Until It Doesn’t

Switching to Weather - By Xiaomi Means Relearning Your Forecast Routine

Ludo King and the Social Life of a Lucky Six
Capture the account carefully and keep the purpose clear
The first useful organizational step is to connect only the account or accounts I genuinely need. That keeps the app understandable and reduces the chance of approving the wrong request. In a workplace, I would label the purpose mentally as “company sign-in” rather than treating the app as a storage place for every account I own.
This is one difference from a typical password manager. A password manager is designed to collect credentials, generate passwords, and fill forms. Salesforce Authenticator is focused on the additional verification stage. If my main goal is to manage dozens of passwords across shopping, banking, email, and work, I would choose a dedicated password manager first and use this app for the account flow it supports.
There is also a useful separation between authentication and account recovery. The app can help verify a legitimate sign-in, but I should still know how my organization handles a lost phone, a replaced device, or a locked account. Those situations are not reasons to avoid two-step verification; they are reasons to understand the recovery process before I need it.
For a small team, this makes onboarding more predictable. I would give a new colleague time to connect the app and perform a test sign-in before removing access to an older method. For an individual user, the same idea applies: do not wait until a device change forces the issue. A security routine should include both everyday approval and occasional account-maintenance checks.
A repeatable routine is more valuable than constant attention
Once connected, the app should become a short checkpoint in the sign-in routine. I enter my normal credentials, look at the request, compare it with what I am doing, and approve only when the context makes sense. That sequence is simple enough to repeat without turning every login into a long security ceremony.
I like this approach because it keeps the extra protection visible. A text message code can work, but it asks me to switch to messages, read a code, return to the login screen, and type it accurately. An authenticator-based approval can feel more direct. The trade-off is that the phone becomes an important part of the workflow, so I need to keep it available and usable when I work.
A realistic example is a remote employee starting the morning from a home laptop. The employee signs in to a Salesforce service, receives a request on the phone, checks that the request matches the action just started, and approves it. Later, while away from the desk, an unexpected request appears. The correct response is to reject or ignore it and investigate, not to approve it simply because the notification looks familiar.
That second scenario is where the app provides more value than convenience alone. The prompt creates a moment to notice suspicious activity. It cannot determine my intentions for me, and it cannot make social-engineering attacks disappear, but it gives me a clear opportunity to question a login that I did not initiate.
For regular use, I would keep the phone’s notification behavior practical rather than overly aggressive. If requests are easy to miss, the workflow becomes frustrating. If every alert is treated as harmless background noise, the security benefit weakens. The right routine is one in which I notice authentication requests without feeling compelled to approve them automatically.
Where the smooth experience can fail
The main weakness is dependence on the phone. A dead battery, a misplaced device, a broken screen, or a notification that does not arrive can interrupt access even when I know the correct password. This is not a flaw unique to this app, but it is a real trade-off that should influence how a business prepares its users.
I would not make the phone the only untested route into an important account. Before traveling or changing devices, I would confirm the organization’s recovery procedure and know whom to contact. The exact options depend on the account administrator and the company’s security setup, so planning matters more than assuming the app will solve every access problem.
Another friction point is the danger of approval fatigue. If a user receives frequent prompts and accepts them without checking, the extra step becomes a ritual with little thought behind it. The app is strongest when the user recognizes the login context. It is weaker when people have been trained to approve every request just to get work done.
Shared devices and shared accounts can also complicate the experience. A personal phone is easier to associate with one person’s sign-ins. In a team environment, I would avoid informal sharing of authentication devices and instead follow the organization’s account-management process. Clear ownership makes suspicious requests easier to recognize and legitimate access easier to support.
Device changes deserve special care. Moving to a new phone is not merely an app-install task when the old phone is part of the verification chain. I would arrange the transition while the old device still works, test the new setup, and keep the relevant support details available. That small amount of preparation can prevent a routine upgrade from becoming an account-lockout problem.
There is also a usability trade-off for people who move constantly between locations or work with unreliable connectivity. An approval-based workflow may be less comfortable when the phone cannot reliably receive requests. In that situation, the best alternative may be another authentication method supported by the organization, rather than abandoning two-step verification altogether.
How it compares with codes, passwords, and broader security apps
Compared with password-only sign-in, Salesforce Authenticator adds a meaningful barrier. A password can be copied, reused, or exposed without the owner noticing. A separate approval request gives the owner a chance to stop a login. It does not remove the need for a strong, unique password, but it makes password theft less decisive.
Compared with text-message codes, the experience can be less tedious because I do not have to transcribe a short number during every sign-in. That convenience comes with a different dependency: instead of relying on the phone network and message delivery, I rely on the authenticator workflow and the phone itself. Neither approach is perfect, so the better choice depends on the organization’s supported methods and the user’s daily conditions.
Compared with a general authenticator app, this product is most compelling when my workplace already uses Salesforce’s identity and security workflow. A general-purpose app may be more versatile for someone protecting unrelated services from different providers. Salesforce Authenticator is a more focused choice for users whose sign-in process is centered on Salesforce accounts and business access.
Compared with a password manager, it solves a different problem. A password manager reduces the temptation to reuse passwords and speeds up credential entry. This app adds confirmation after or alongside that credential step. For a well-rounded system, I would see them as complementary rather than competing tools, provided the organization allows both.
Small practices that make the setup more dependable
Complete a real test sign-in immediately after connecting the account, while assistance is still easy to reach.
Read every unexpected request as a possible warning, especially when I am not actively signing in.
Plan a device-change or lost-phone procedure before traveling, upgrading hardware, or handing a phone in for repair.
Keep the authenticator’s role separate from password storage and account recovery so I know which tool to use in each situation.
Teach colleagues that approving a request is an identity decision, not merely the final step in a login.
These practices are more useful than simply installing the app and forgetting about it. They address the points where authentication systems usually become unreliable: rushed approvals, unplanned device changes, unclear ownership, and confusion about recovery.
Who should adopt it, and who should look elsewhere
I would recommend Salesforce Authenticator to Salesforce users, employees, and small teams who want a straightforward second step around business sign-ins and who can keep a personal, working phone available. It is especially suitable for people who prefer approving a request over copying a code and for organizations that want users to notice unusual login attempts.
It is also a sensible fit for a business trying to build a sustainable productivity system. Security should not be an emergency project that interrupts work every few months. A short, repeatable approval habit can sit naturally beside the morning sign-in routine, device-management checklist, and periodic account review.
I would be more cautious about recommending it as someone’s only authentication solution across an entire digital life. If the main need is protecting many unrelated consumer accounts, a broader authenticator or password manager may offer a better overall system. If a user regularly loses access to a phone, ignores notifications, or cannot arrange account recovery support, the workflow may become more frustrating than helpful.
The app also requires a certain level of attention. People who approve every prompt without checking the context are not getting the full benefit. In that case, training and account policy matter as much as the app itself. The technology can present the decision, but the user still has to make it carefully.
My final view after fitting it into everyday work
Salesforce Authenticator is a focused business security app rather than an all-purpose account utility. I appreciate that its value is easy to understand: it adds a second confirmation step to a sign-in and makes unexpected requests visible. The experience is most comfortable when the phone is nearby, notifications are dependable, and the account’s recovery process has already been considered.
Its limitations are equally clear. It can interrupt access when the phone is unavailable, and it cannot protect users who approve requests mechanically. It also does not replace password management, device planning, or good account administration. Those are not reasons to dismiss it; they define the system that needs to surround it.
With that context, I think it is a worthwhile free choice for the right audience. I would install it as part of a planned Salesforce sign-in workflow, test it before depending on it, and teach myself to question every unexpected prompt. Used that way, it adds security without turning ordinary work into a complicated process.
Pros
- Provides strong two-factor authentication for Salesforce accounts.
- Push notifications make sign-ins quick and convenient.
- Supports biometric approval on compatible devices.
- Can generate verification codes without a mobile signal.
- Helps protect accounts from stolen or reused passwords.
Cons
- Requires access to the registered phone during sign-in.
- Changing or losing devices may require account recovery steps.
- Push approvals can be confusing when sign-in details are limited.
- Battery usage may increase slightly from background notifications.
- Best suited to Salesforce users, with limited value elsewhere.
FAQs for Salesforce Authenticator
What is Salesforce Authenticator and what is it used for?
Salesforce Authenticator is a mobile security app that adds multi-factor authentication to supported Salesforce accounts and other compatible services. After linking the app to your account, it can send a push notification when a sign-in requires verification. You can review the login details, such as the service and approximate location, and approve or deny the request from your phone.
How do I set up Salesforce Authenticator for my account?
To set up Salesforce Authenticator, install the app on your Android or iOS device and open it. The service you are securing will usually display a QR code or a two-word connection phrase. Follow the on-screen instructions to link the account, then complete a test verification. Keep your phone nearby and make sure notifications and internet access are enabled during setup.
Does Salesforce Authenticator work without an internet connection?
Salesforce Authenticator generally needs an internet connection to receive and respond to push notifications, so offline use can be limited. Depending on the organization’s Salesforce configuration, you may have an alternative verification method, such as a one-time passcode or another approved authenticator. Before relying on the app while traveling, confirm which backup options your administrator provides.
What should I do if I lose my phone or get a new device?
If your phone is lost, stolen, replaced, or reset, contact your Salesforce administrator or IT support as soon as possible so they can disconnect the old authenticator and help you register a new one. Do not approve unexpected login requests. If you still have access to the old device, use the account’s available transfer or backup process, but follow your organization’s security policy first.
Is Salesforce Authenticator free and is it safe to use?
Salesforce Authenticator is typically available as a free mobile app, although access to the protected Salesforce service depends on your organization’s account and security settings. It improves security by requiring an additional verification step and showing useful sign-in information before approval. You should still protect your phone with a passcode, keep the app updated, and deny requests you do not recognize.

Salesforce Authenticator
This site provides independent information about third-party apps and is not affiliated with, or the owner, developer, or distributor of, any app featured here. App names, logos, and trademarks belong to their respective owners. Developer details are provided for reference; please contact the developer directly via authenticator-feedback@salesforce.com, visit http://www.salesforce.com, or review their http://www.salesforce.com/company/privacy/full_privacy.jsp.










